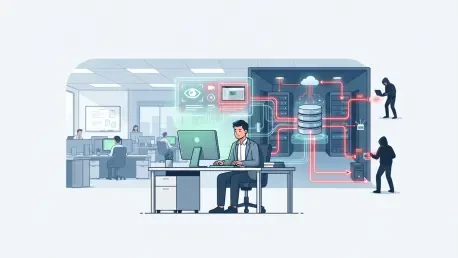
The global landscape of professional environments has transitioned into a complex ecosystem where remote and hybrid work models are no longer the exception but the standard expectation for the modern workforce. This shift has inadvertently triggered a surge in the deployment of invasive “bossware” tools as organizations scramble to maintain the same level of oversight once provided by a physical office presence. However, the adoption of these surveillance technologies introduces a profound irony: the very systems implemented to protect corporate productivity and digital assets often become the most vulnerable entry points for sophisticated cyberattacks. These tools, which function by capturing every keystroke, screen movement, and webcam feed, create a massive repository of sensitive data that acts as a magnet for malicious actors. While executives may believe they are securing their operations, they are frequently trading long-term structural integrity for a short-term illusion of control. The result is a growing concern among cybersecurity experts that the risk-to-reward ratio of monitoring software has reached a critical tipping point, where the threat to data privacy and network security far outweighs any marginal gains in observed employee efficiency or task management. The exposure risk was recently highlighted by the 2025 WorkComposer incident, where an unsecured cloud bucket leaked over 21 million screenshots containing private messages and confidential documents, proving that the harvest of such data is a liability waiting to be exploited.
Significant Technical Vulnerabilities: The Risk of Elevated Permissions
Monitoring tools are not just passive observers; they are deeply integrated system components that require elevated privileges to function effectively without being terminated by the end user. To prevent employees from manually closing monitoring processes or using task managers to end surveillance, these applications often demand “root” or administrative access, which grants them the ability to bypass standard security sandboxes. This broad permission set essentially creates a universal key for the device and, by extension, the entire corporate network. If an attacker manages to exploit a vulnerability within the monitoring software itself, they inherit these administrative privileges, allowing them to install ransomware, exfiltrate data, or disable internal defenses with minimal resistance. This high-level access has even caused internal friction within tech giants, such as during the 2026 Model Capability Initiative, where excessive data visibility led to unauthorized internal access despite widespread employee opposition. A single misconfiguration in the vendor’s cloud storage or a breach of the management console can result in the exposure of millions of records, turning a tool meant for oversight into a catastrophic liability that facilitates identity theft and corporate espionage through the capture of active session tokens and passwords.
Beyond the risks of elevated permissions, the functional behavior of monitoring software frequently mirrors the tactics used by advanced persistent threats and spyware, creating significant friction with existing security infrastructure. Because these tools actively record screens, log keystrokes, and monitor background processes, they often trigger legitimate warnings from antivirus programs and Endpoint Detection and Response (EDR) platforms. In many instances, IT departments are pressured to create permanent exceptions or “whitelist” the monitoring software to prevent it from being quarantined or blocked. This creates a dangerous technical blind spot where malicious actors can disguise their malware to mimic the behavioral signatures of the authorized monitoring agent. Security teams, already overwhelmed by high volumes of data, eventually suffer from “alert fatigue,” where they become desensitized to warnings involving surveillance behaviors. This environment allows genuine intrusions to go unnoticed for extended periods, as the very presence of bossware establishes a precedent for suspicious activity that is tolerated rather than investigated. Consequently, the organization loses the granular visibility into network anomalies required to stop a sophisticated breach before it escalates into a full-scale crisis.
Human Factors: Social Engineering and Supply Chain Exposure
The psychological impact of constant workplace surveillance extends beyond morale, fundamentally altering how employees perceive and respond to digital security threats in their daily routines. In an environment where workers are conditioned to expect frequent, invasive IT oversight and “security checks” from their employers, they become significantly more susceptible to social engineering attacks. Scammers often take advantage of this compliance by impersonating help desk staff or sending fraudulent software update prompts that mimic the routine communications sent by internal management. Because remote employees lack the ability to quickly verify a suspicious request with a colleague across a desk, they are more likely to provide credentials or grant remote access under the guise of “mandatory system maintenance.” Research into employee behavior indicates that a substantial portion of remote workers cannot distinguish between a legitimate security protocol and a phishing attempt, particularly when the request arrives during a time when they are already feeling the pressure of being monitored. This conditioned obedience erodes the human firewall that is supposed to serve as the last line of defense, making the workforce an unintentional gateway for external threats targeting the internal network.
Organizations rarely possess the resources to develop proprietary monitoring solutions, leading to a heavy reliance on third-party vendors whose security practices may not align with corporate standards. This creates a significant supply chain risk, as a company’s data security is effectively outsourced to an entity that may prioritize rapid feature deployment over robust protection. When a vendor manages the collection and storage of sensitive employee metrics, the hiring organization loses direct visibility into who has access to that data or how effectively it is being shielded from external breaches. While certifications like SOC2 are often touted as proof of reliability, they frequently only provide a snapshot of a vendor’s security posture at a specific point in time rather than ensuring continuous adherence to high standards. Historical data suggests that a large portion of documented corporate attacks originate from weaknesses in the third-party ecosystem, and monitoring vendors are especially vulnerable due to the immense value of the data they hold. If a vendor experiences a breach, the hiring company remains legally and reputationally responsible for the loss of employee information, despite having no direct way to prevent the incident or control the response.
Operational Consequences: Shadow IT and the Regulatory Landscape
A counterproductive and dangerous trend arising from invasive monitoring is the widespread adoption of “shadow IT” and evasion software by employees seeking to reclaim a sense of privacy. When workers feel that their every second is being scrutinized, they often turn to unauthorized tools such as hardware “mouse jigglers” or software scripts designed to simulate digital activity. The danger of this behavior is twofold: not only does it render the gathered productivity data entirely useless, but it also introduces unvetted and potentially malicious code into the corporate environment. A 2025 investigation revealed that even government agencies were not immune, with over 120 individuals found using such tools to bypass activity tracking. These evasion tools are typically not found in official company application stores and are often downloaded from obscure forums or unverified websites where they are frequently bundled with credential-stealing malware or trojans. Since these tools are meant to hide from the monitoring software, they are also designed to be difficult for IT departments to detect. This creates a hazardous cycle where the very attempt to enforce productivity leads to a situation where unmanaged software is running on corporate devices, providing a backdoor for attackers.
As 2026 progresses, the legal landscape surrounding workplace surveillance is undergoing a rapid transformation to address the ethical and security concerns of automated oversight. Lawmakers in various states, notably California and Connecticut, have implemented rigorous regulations that limit the use of artificial intelligence and monitoring tools in making critical employment decisions. These new laws emphasize transparency and require organizations to provide clear justifications for disciplinary actions, specifically prohibiting the “black box” approach where automated algorithms determine an employee’s fate without human intervention. This shift in the regulatory climate means that companies relying on invasive monitoring may face increased legal liabilities under labor protections if they cannot demonstrate a direct link between the data collected and actual job performance. Furthermore, the risk of litigation increases significantly when monitoring data is mishandled or used in a discriminatory manner, whether intentionally or through algorithmic bias. This evolving legal framework forces organizations to reconsider the long-term sustainability of invasive surveillance, as the potential for regulatory fines and lawsuits begins to eclipse the perceived benefits of digital tracking.
Strategic Transitions: Shifting Toward Trust and Outcome Management
The accumulation of technical vulnerabilities and cultural friction has led to a paradigm shift among high-performing organizations toward outcome-based management rather than minute-by-minute activity tracking. This strategy recognizes that the true value an employee provides is found in the quality and timeliness of their deliverables rather than the volume of their digital footprints. By shifting the focus away from “active minutes” and keystroke logs, managers can foster a culture of autonomy and trust that has been shown to improve both employee retention and overall engagement. This approach not only eliminates the need for high-risk monitoring software but also simplifies the management process by setting explicit expectations and providing clear channels for structured communication. When employees understand the specific goals they are expected to achieve, the ambiguity that often drives managers to adopt surveillance tools is removed. This transition results in a leaner, more focused management structure where performance is measured by results, allowing the organization to operate more effectively without the overhead and risk associated with pervasive digital oversight.
The decision to prioritize data minimization and human-centric leadership proved to be the most effective strategy for securing the digital perimeter during this era of remote work. Organizations that moved away from invasive surveillance managed to reduce their overall attack surface by eliminating high-risk data stores and restoring the integrity of their internal security alerts. This transition fostered a resilient workforce that felt empowered rather than policed, which directly translated into higher levels of loyalty and a more proactive stance toward identifying genuine security threats. To maintain this progress, IT departments adopted rigorous auditing processes for existing tools and established strict boundaries for data collection, ensuring that only information essential to core business operations was retained. Leadership teams implemented regular, transparent check-ins that replaced automated tracking, allowing for the identification of roadblocks through dialogue rather than surveillance. Ultimately, the industry realized that the most secure organizations were those that valued the human element above all, recognizing that trust was a more powerful driver of productivity and security than any monitoring application could ever provide.