Acting as a gateway in the mail path allows continuity systems to function independently when primary cloud provider APIs experience catastrophic failure. The massive Microsoft 365 outage of November 12 served as a wake-up call for organizations worldwide, exposing the inherent fragility of modern enterprise communication. When Outlook, Teams, and SharePoint went offline for nearly 24 hours, global operations ground to a halt, leaving millions of users disconnected. This event demonstrated that relying solely on a single cloud provider creates a dangerous single point of failure that can paralyze a business within minutes. Traditional Service Level Agreements are often mistaken for disaster recovery plans, yet they offer no technical relief during a crisis. While an SLA might provide financial credits after a service failure, it cannot restore lost productivity or repair damaged client relationships. Achieving true resilience requires a proactive strategy that moves beyond financial compensation toward technical independence and operational continuity during critical system failures.
The Challenge: Addressing Single Provider Dependency
The modern business environment is heavily centralized, making many companies vulnerable to the stability of a single platform. When a primary provider fails, organizations lose more than just the ability to send mail; they lose access to administrative dashboards, status alerts, and internal coordination tools. This creates a “blackout” effect where IT teams cannot even diagnose the extent of the problem because their primary communication channels are also down. In the period from 2026 to 2028, the industry witnessed a significant rise in these types of cascading failures, proving that even the most robust cloud infrastructures are not immune to global logic errors. The isolation experienced during these outages often leaves management teams in the dark, unable to broadcast updates to their workforce or provide clear guidance to concerned stakeholders. Without a secondary path for information to flow, the silence from the provider becomes a deafening obstacle to effective incident response and crisis management.
To mitigate this risk, businesses must shift away from the “all eggs in one basket” approach that has dominated IT strategy for the past decade. A resilient infrastructure utilizes an independent, always-on safety net that operates entirely outside the primary provider’s ecosystem. This secondary path ensures that if the main platform experiences a regional or global failure, the organization can continue its essential functions without waiting for the provider’s engineers to resolve the issue. This strategy requires a mindset shift from reactive recovery to proactive persistence, where the goal is not just to fix the problem but to remain operational while the problem exists. Organizations that successfully decoupled their communication layers from their core service providers found themselves much better equipped to handle the unexpected volatility of the cloud landscape. By diversifying their technology stack, these firms transformed their vulnerability into a competitive advantage, ensuring that their client-facing operations remained steady and reliable regardless of external technical shocks.
Architectural Choice: Implementing Gateway Resilience
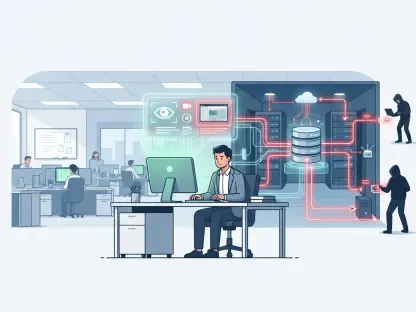
The most effective way to ensure email persistence is through a gateway-based architecture rather than an API-only integration. Many security tools connect directly to Microsoft or Google via APIs, meaning that if the host platform crashes, the security and continuity tools crash with them. A gateway sits in the mail path, allowing it to capture and process data independently of the primary cloud environment’s health. This positioning is critical because it creates a buffer between the internet and the enterprise mail server. When the destination server goes dark, the gateway remains standing, intercepting incoming traffic and queuing it for later delivery while providing an alternative interface for users to access their messages. This design philosophy ensures that the continuity layer is not a “guest” on the platform it is meant to protect, but rather an independent guardian that maintains its own uptime and operational logic. This architectural separation is the cornerstone of any truly resilient disaster recovery strategy in the modern era.
This system functions through constant journaling and synchronization, where every message is intercepted, encrypted, and stored in a secondary environment. Because this process is “always-on,” there is no manual switch to flip or failover trigger required when an outage begins. This architectural choice eliminates the risk of human error and the inevitable delays associated with emergency IT interventions during a high-stress service disruption. Administrators no longer need to scramble to redirect MX records or change complex configurations under the pressure of a global downtime event. Instead, the transition is seamless and immediate, with the secondary environment already containing the necessary data to keep the business moving. By automating the persistence layer, companies can reduce their recovery time objective to nearly zero, ensuring that the impact of a provider outage is felt only as a change in the user interface rather than a total loss of functionality. This level of automation is essential for maintaining trust in digital communication systems.
Operational Continuity: Maintaining Productivity and Security
When a primary mail service is unavailable, employees need immediate access to a functional workspace. A resilient solution provides a secure web-based client that allows users to send and receive messages from any browser on any device. This bypasses the need for desktop applications like Outlook, which may be unresponsive or tethered to the failing cloud infrastructure, ensuring that staff can resume work instantly. Continuity is not just about new messages; it also requires access to historical context. Effective systems maintain an “emergency inbox” containing the most recent 30 days of email data and attachments. By providing this recent history, the system ensures that employees have the information they need to continue ongoing projects and respond to client inquiries without interruption, maintaining a professional front even during a technical crisis. This continuity of access prevents the total paralysis of departments like sales and customer support, where having the latest communication history is vital for closing deals and solving issues.
Security should never be sacrificed for the sake of availability, especially during an outage when organizations are most vulnerable. A robust continuity service maintains the company’s security posture by applying Data Loss Prevention, threat protection, and encryption policies to all mail sent during the fallback period. This ensures that sensitive information remains protected and that the company stays compliant with industry regulations throughout the incident. Once the primary cloud provider restores service, the transition back to normal operations must be seamless. An automated reconciliation process routes all messages sent and received during the outage back to the user’s primary inbox and sent items folders. This eliminates the need for manual data entry or cleanup tasks, allowing the workforce to return to their standard workflow with a complete and chronological record of all communications. This bidirectional synchronization is what separates a true professional continuity tool from a simple backup service, as it preserves the integrity of the corporate record.
Internal Systems: Securing Flow and Applications
While external communication with clients is vital, internal email is the engine that drives organizational productivity. Advanced continuity models utilize exchange journaling to allow colleagues to communicate with one another even when the central cloud infrastructure is completely offline. This ensures that internal departments can coordinate their response to the outage and maintain business processes that rely on inter-office cooperation. During major outages, the inability to communicate internally often causes more damage than the loss of external mail, as it breaks the chains of command and stops the flow of internal approvals. By preserving the internal flow, organizations can manage the crisis from within, keeping teams aligned and informed as they work through the disruption. This internal resilience is a critical component of business logic that often goes ignored until a failure occurs, at which point the lack of internal coordination becomes a major liability for the company’s executive leadership.
A significant but often overlooked vulnerability is the failure of machine-generated and application mail, such as password resets, automated invoices, and shipping alerts. These messages often share the same path as human email and fail simultaneously during a cloud disruption. By using a secure email relay to separate application traffic from user mailboxes, companies can ensure that their automated systems remain functional, preserving critical business logic and customer notifications during a platform outage. This separation allows for higher deliverability and better security for automated mail, while ensuring that the “plumbing” of the business continues to work even if the “human” interface is down. Protecting these automated workflows is essential for maintaining customer trust, as a failure to send an invoice or a shipping notification can lead to significant downstream logistical problems. Secure email relays provide a dedicated, hardened path for these messages, ensuring they are not caught up in the same infrastructure failures that plague standard user mailboxes.
Strategic Compliance: Independent Archiving and Lessons
Legal and compliance obligations remain in effect even when a cloud provider is down. Organizations must maintain a cloud-native archive that sits outside their primary platform to serve as an independent system of record. This archive should provide “Write Once, Read Many” compliant preservation, ensuring that data residency requirements and legal holds are preserved regardless of the status of the primary email provider. An independent archive also facilitates eDiscovery and internal audits during a crisis. If legal teams or administrators need to access historical data while the primary service is offline, a third-party archive ensures that this information remains searchable and retrievable. This layer of redundancy protects the organization from legal risks and data loss, providing a permanent and immutable history of all corporate communications. By separating the archive from the operational mail system, businesses ensure that their historical record is never held hostage by the uptime of a single vendor’s cloud infrastructure.
The November outage highlighted the high cost of being unprepared, as seen in companies that had to enable continuity services in the middle of the crisis. One global payroll firm discovered that while they could restore human communication, their automated tax and payroll alerts remained offline because they were still tied to the failing provider. This realization forced a strategic shift toward diversifying their mail paths to avoid future disruptions. These real-world examples proved that outages often exposed hidden dependencies that were only recognized when they failed. Organizations that had already implemented a secondary path successfully processed millions of messages without a lapse in service. For these proactive companies, the outage was a minor technical footnote rather than a catastrophic business event, validating their investment in a multi-vendor infrastructure strategy. The transition toward independent continuity solutions marked a new era of digital maturity, where resilience became the primary metric for evaluating the success of enterprise communication systems.